MPs are worried that China can remote control cars in the UK
The UK’s Business and Trade Commission has called on UK telecom firms to begin monitoring exactly what data is being collected and sent by popular Chinese vehicles.
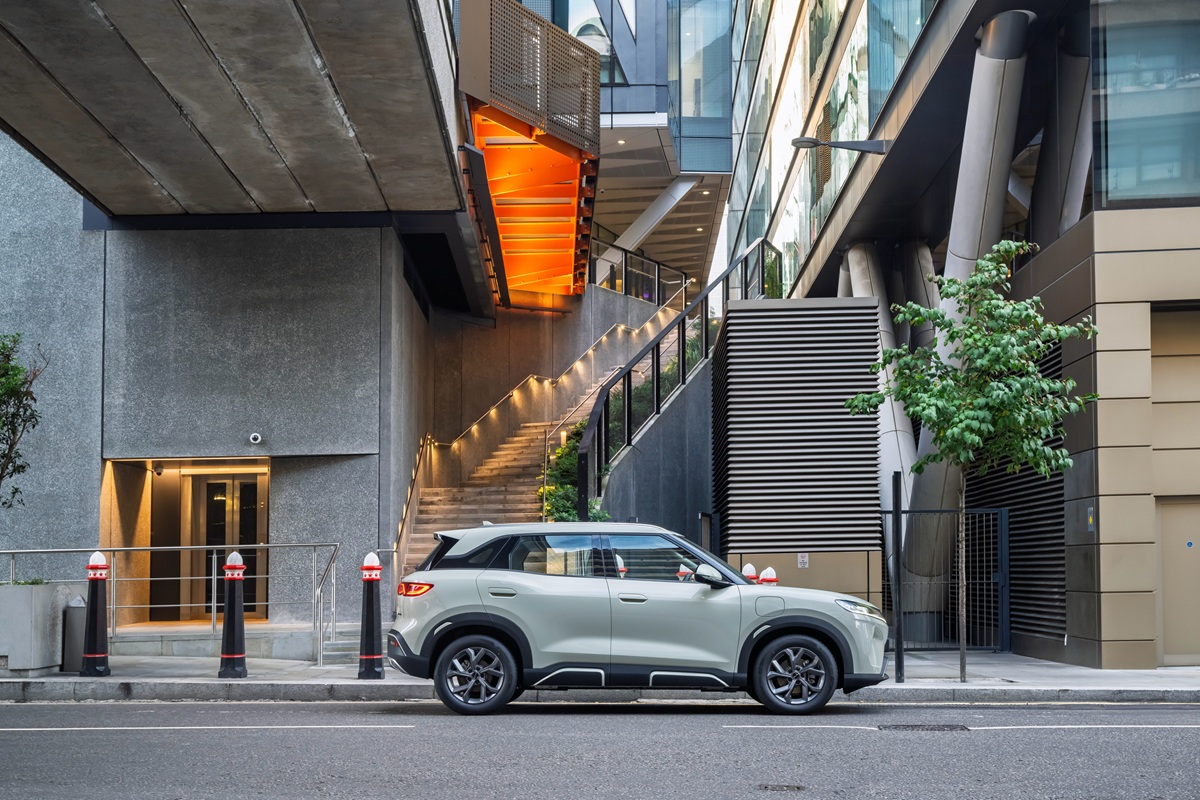
In a new report published on Monday (2 November), the Commission noted that Chinese car brands’ UK market share doubled between March 2025 and March 2026. In 2025 alone, Chinese-built models accounted for about 30% of the more than 470,000 electric vehicles sold in the UK.
This raises the risk of dependency and increases the UK’s vulnerability to economic coercion and geopolitical disruption, the Commission noted.
“Manufacturers can send data to connected devices via over-the-air (OTA) updates. This creates the risk of manufacturers controlling or disabling (‘bricking’) the devices remotely. The remote control of connected vehicles is a particular vulnerability, given the potential risk to life,” the report states.
Remote control cars
The Commission cited Tor Indstøy, VP, Risk Management and Threat Intelligence at Norwegian telecoms firm Telenor who found that a Chinese-made Yutong bus had critical functions connected to the internet.
This allows for ‘direct digital access for OTA (over-the-air) updates and diagnostics’. The bus was found to have a component with a cellular modem that can be used for direct access to the battery or the engine system. This means that the buses can be stopped or manipulated directly from China
The Committee also raised concerns that Chinese security services could require China-based manufacturers to grant access to such systems and use this access to disrupt foreign countries’ transport and logistics systems.
Finally, the report raised concerns that connected vehicles are also vulnerable to hacks by malicious non-state actors, who might then control or degrade the vehicles remotely. However, the risk does not stem entirely from the use of Chinese components.
Professor Ciaran Martin, former CEO of the UK’s National Cyber Security Centre, highlighted recent Chinese digital attacks against the US (‘Salt Typhoon’ in 2023 and ‘Volt Typhoon’ in 2024) “had nothing to do with Chinese kit” but were rather facilitated by “vulnerable western manufactured infrastructure”.
He added that “China has not activated any of its digital booby traps yet, and according to the US Government, there is no sign that it intends to”.
Broader data concerns
Connected devices contain sensors – such as audio sensors and internal and external cameras on connected vehicles – that collect user data. They also contain components such as cellular or Wi-Fi modules that enable this data to be transmitted to the manufacturer.
Chinese manufacturers must by law cooperate with the Chinese state to assist with what the state considers to be national security matters. The Chinese state therefore has potential access to vast quantities of foreign data, which it could use to exploit vulnerabilities (cyber or otherwise) in states it views as its competitors or adversaries.
Hackers can also exploit connected devices to collect data, because these do not always transfer data securely. Tor Indstøy found that his electric car was sending most data traffic to a Beijing-based server that supported the use of outdated encryption technology, known for its weaknesses.
The Committee warned that a hacker or hostile state could use data gathered from connected devices such as drones, vehicles, or solar inverters to steal commercially sensitive information from UK firms, build an intelligence picture of the UK’s critical national infrastructure, or to intimidate and coerce individuals